FakeGit malware campaign returns with 17,610 malicious GitHub repos
- October 8, 2026
- 01:10 PM
- 0
More than 17,000 fake repositories on GitHub are distributing the SmartLoader malware after the FakeGit campaign reactivated earlier this month to push the StealC infostealer.
The operator uses mostly throwaway accounts, but researchers identified at least 700 accounts that appear to belong to legitimate developers.
The malicious repositories use convincing README instructions with a download button pointing to a ZIP archive containing the initial payload, SmartLoader, that is used to distribute other malware.
While similar activity with various payloads has been observed since at least January, the FakeGit term was associated with this operation in July, when researchers at enterprise browser platform Island published a report on 7,600 fake GitHub repositories pushing the SmartLoader malware.
Island noted at the time that 800 of the malicious repositories masqueraded as AI skills or MCP servers that appeared in public AI registries and catalogs.
A new report from researchers at software supply-chain security platform Apiiro says that FakeGit resumed its activity on October 4 and now uses 17,610 repositories on GitHub.
In just 34 hours, FakeGit pushed more than 13,000 repos, peaking at 2,999 an hour.
"In the commits we sampled, 97% touched only the README, and 88% pointed its “Download” button at a ZIP that installs SmartLoader," Apiiro says.
"Nobody had to create a single new repo. The fleet was already there. It just got re-aimed," the researchers added.
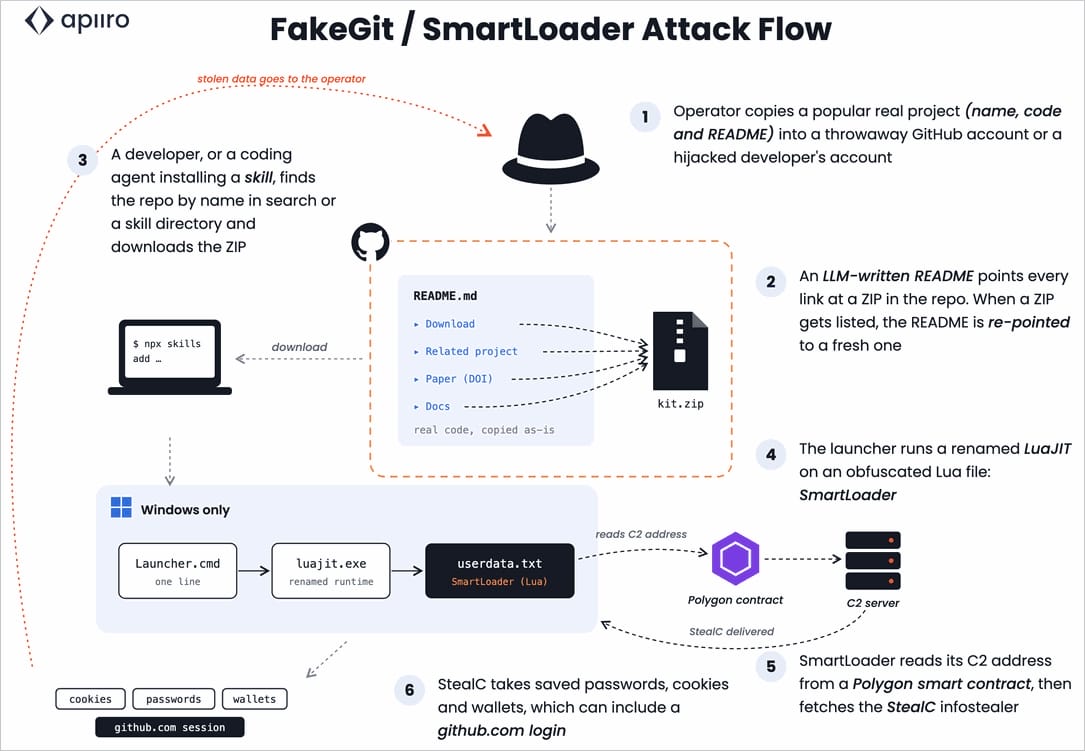 FakeGit attack flow
Source: Apiiro
How FakeGit survived
According to the researchers, the reason behind FakeGit's survival is that removing repositories is based on lists that cover only a fraction of the malicious repos.
Also, blocklisted payloads and backup copies remain accessible, so attackers can simply change the download links while keeping the same repositories active.
“71% of the fleet was missing from URLhaus before our report, and a domain-level DNS blocklist can’t block one file on GitHub without blocking GitHub,” Apiiro explains.
The researchers found malicious archives in forks, older files, release assets, issue attachments, and separate download-hosting repositories, which makes deleting one link at a time ineffective.
“Delete one file and the operator can point the lure at a spare copy: a fork, an older ZIP, a release asset or an issue attachment,” the researchers said.
Apiiro researchers recommend that users verify the repository’s owner. Furthermore, the source for installing AI skills and MCP servers should be official registries or vendor repositories.
If SmartLoader execution is suspected, users should treat the incident as a potential GitHub account compromise, revoke active sessions and access tokens, and move to passkeys.
.article-callout { background-color: #f0f6ff; width: 95%; max-width: 800px; margin: 15px auto; border-radius: 8px; border: 1px solid #d6ddee; display: flex; align-items: stretch; overflow: hidden; } .article-media { flex: 1; max-width: 220px; display: flex; } .article-media a { display: flex; width: 100%; height: 100%; } .article-media img { width: 100%; height: 100%; border-radius: 8px 0 0 8px; display: block; } .article-callout .article-media img { margin-top: 0 !important; height: 100% !important; } .article-body { flex: 2; padding: 10px; display: flex; flex-direction: column; justify-content: center; } .article-body h2 { font-size: 17px !important; font-weight: 700; color: #333; line-height: 1.4; font-family: Georgia, "Times New Roman", Times, serif; margin: 0 0 14px 0; } .article-body p { font-weight: bold; font-size: 14px; margin: 0 0 clamp(6px, 2vw, 14px) 0; } .article-link { background-color: #fff; border: 1px solid #3b59aa; color: black; text-align: center; text-decoration: none; border-radius: 8px; display: inline-block; font-size: 16px; font-weight: bold; padding: 10px 20px; width: fit-content; } @media (max-width: 600px) { .article-callout { flex-direction: column; align-items: center; } .article-media { max-width: 100%; } .article-media img { border-radius: 8px 8px 0 0; } .article-body { padding: 15px; width: 100%; } .article-link { width: 100%; margin: 0 auto; box-sizing: border-box; } }
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Save your seatRelated Articles:
Over 543,000 valid credentials exposed in public GitHub repositories
GitHub Actions re-enabled with Mini Shai-Hulud payload still active
Fake LastPass Authenticator GitHub repos push new Rapuncel infostealer
Malicious npm packages evade install-script defenses at runtime
Was this article helpful?