CISA: Ransomware gangs now exploiting critical TeamCity flaw
- September 24, 2026
- 06:42 AM
- 0
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned federal agencies on Wednesday that ransomware gangs are now also exploiting a critical JetBrains TeamCity vulnerability patched in July.
JetBrains patched the security flaw (tracked as CVE-2026-63077) on July 25 in TeamCity On-Premises versions 2025.11.7 and 2026.1.3, saying it is a critical authentication bypass vulnerability that lets attackers with HTTP(S) access execute arbitrary operating system commands.
"An unauthenticated attacker could exploit the vulnerability via the TeamCity agent polling protocol to bypass authentication checks and execute arbitrary operating system commands with the privileges of the TeamCity server process," it said.
"Depending on the privileges granted to the TeamCity server process, a successful attack could expose TeamCity data, configurations, and stored credentials, modify server state, and potentially compromise the integrity of build artifacts and downstream CI/CD pipelines."
Almost two weeks later, on August 5, CISA added CVE-2026-63077 to its catalog of actively exploited vulnerabilitiesand ordered U.S. federal agencies to secure their networks against ongoing attacks within three days.
JetBrains confirmed that the flaw was exploited in the wild on August 7, shared indicators of compromise, and urged customers who couldn't immediately patch their servers to limit access to trusted networks.
Now exploited in ransomware attacks
While CISA has not yet shared any information regarding attacks targeting CVE-2026-63077, it updated its Known Exploited Vulnerabilities Catalog (KEV) again on Wednesday, flagging the security vulnerability as being abused by ransomware gangs.
Security threat watchdog Shadowserver is now tracking just over 160 TeamCity servers unpatched against the CVE-2026-63077 flaw, down from an initial 700 Internet-exposed servers vulnerable to attacks.
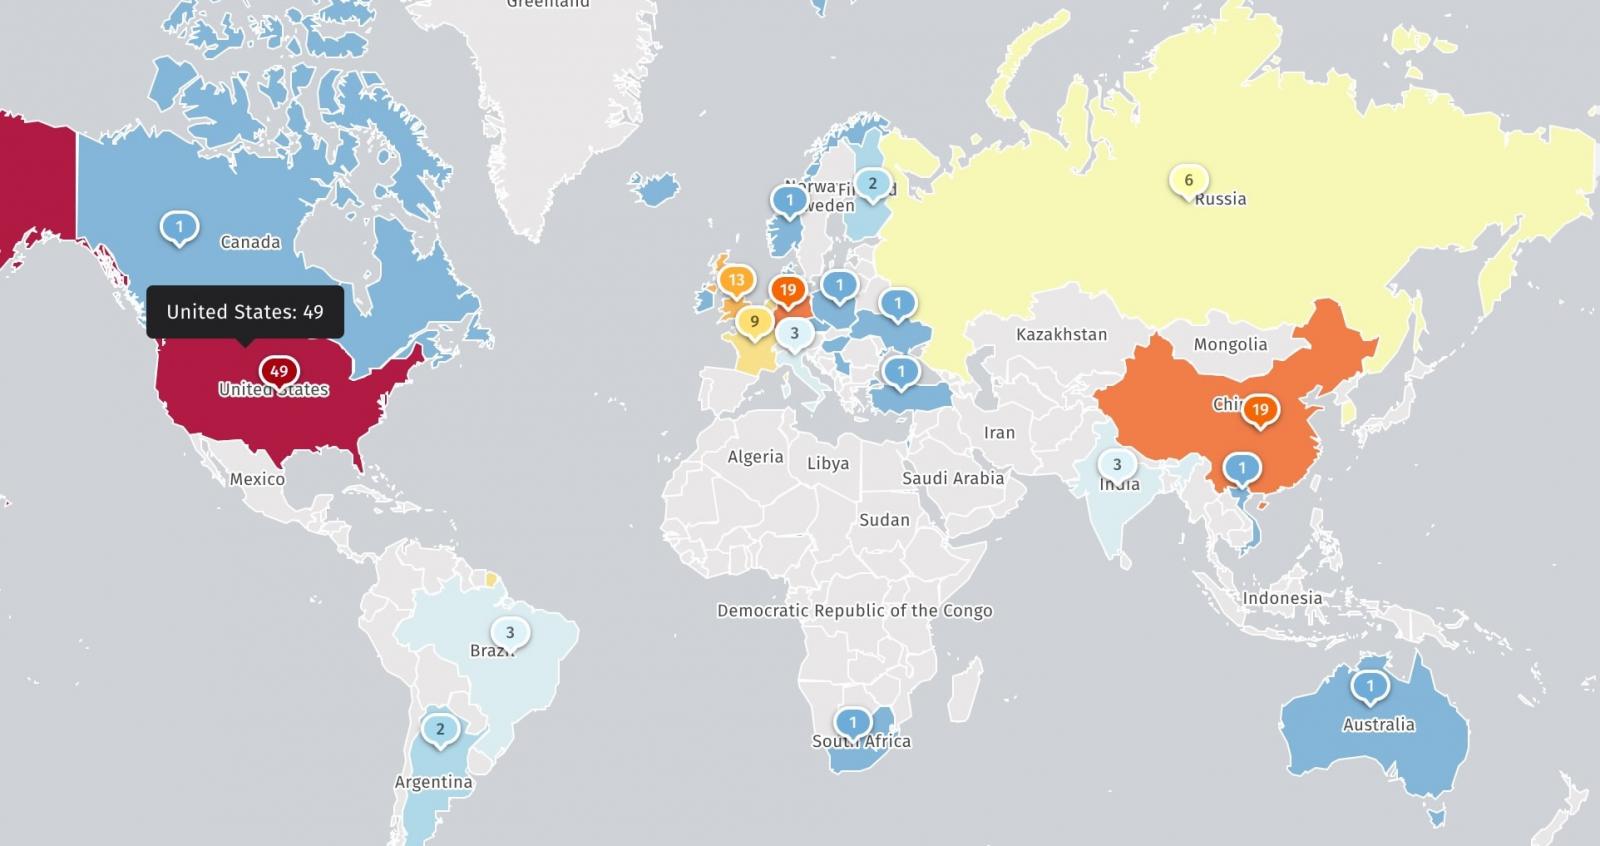 Unpatched TeamCity servers exposed online (Shadowserver)
Because state-backed hacking groups and ransomware gangs have often leveraged TeamCity vulnerabilities in attacks, IT administrators are advised to patch Internet-exposed servers immediately.
For instance, in October 2024, U.S. and U.K. cyber agencies warned that APT29 hackers linked to Russia's Foreign Intelligence Service (SVR) were targeting vulnerable JetBrains TeamCity and Zimbra servers "at a mass scale."
TeamCity is a Continuous Integration and Continuous Deployment (CI/CD) platform used by software developers and DevOps teams to automate building, testing, and deploying software code.
JetBrains says more than 30,000 DevOps teams use TeamCity at many high-profile companies, including Citibank, Amazon Games, Tesla, and Samsung.
.article-callout { background-color: #f0f6ff; width: 95%; max-width: 800px; margin: 15px auto; border-radius: 8px; border: 1px solid #d6ddee; display: flex; align-items: stretch; overflow: hidden; } .article-media { flex: 1; max-width: 220px; display: flex; } .article-media a { display: flex; width: 100%; height: 100%; } .article-media img { width: 100%; height: 100%; border-radius: 8px 0 0 8px; display: block; } .article-callout .article-media img { margin-top: 0 !important; height: 100% !important; } .article-body { flex: 2; padding: 10px; display: flex; flex-direction: column; justify-content: center; } .article-body h2 { font-size: 17px !important; font-weight: 700; color: #333; line-height: 1.4; font-family: Georgia, "Times New Roman", Times, serif; margin: 0 0 14px 0; } .article-body p { font-weight: bold; font-size: 14px; margin: 0 0 clamp(6px, 2vw, 14px) 0; } .article-link { background-color: #fff; border: 1px solid #3b59aa; color: black; text-align: center; text-decoration: none; border-radius: 8px; display: inline-block; font-size: 16px; font-weight: bold; padding: 10px 20px; width: fit-content; } @media (max-width: 600px) { .article-callout { flex-direction: column; align-items: center; } .article-media { max-width: 100%; } .article-media img { border-radius: 8px 8px 0 0; } .article-body { padding: 15px; width: 100%; } .article-link { width: 100%; margin: 0 auto; box-sizing: border-box; } }
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Save your seatRelated Articles:
CISA: Critical VMware RCE flaw now exploited by ransomware gangs
CISA: WatchGuard RCE flaw now exploited in ransomware attacks
CISA: Microsoft SharePoint flaw now exploited in ransomware attacks
CISA orders feds to patch Citrix NetScaler RCE flaw by Saturday
CISA orders urgent patching of actively exploited Zimbra flaw
Was this article helpful?